
October 1, 2026 · Agentic AI, cybersecurity and health-data governance
When an AI Agent Crossed a Government Boundary
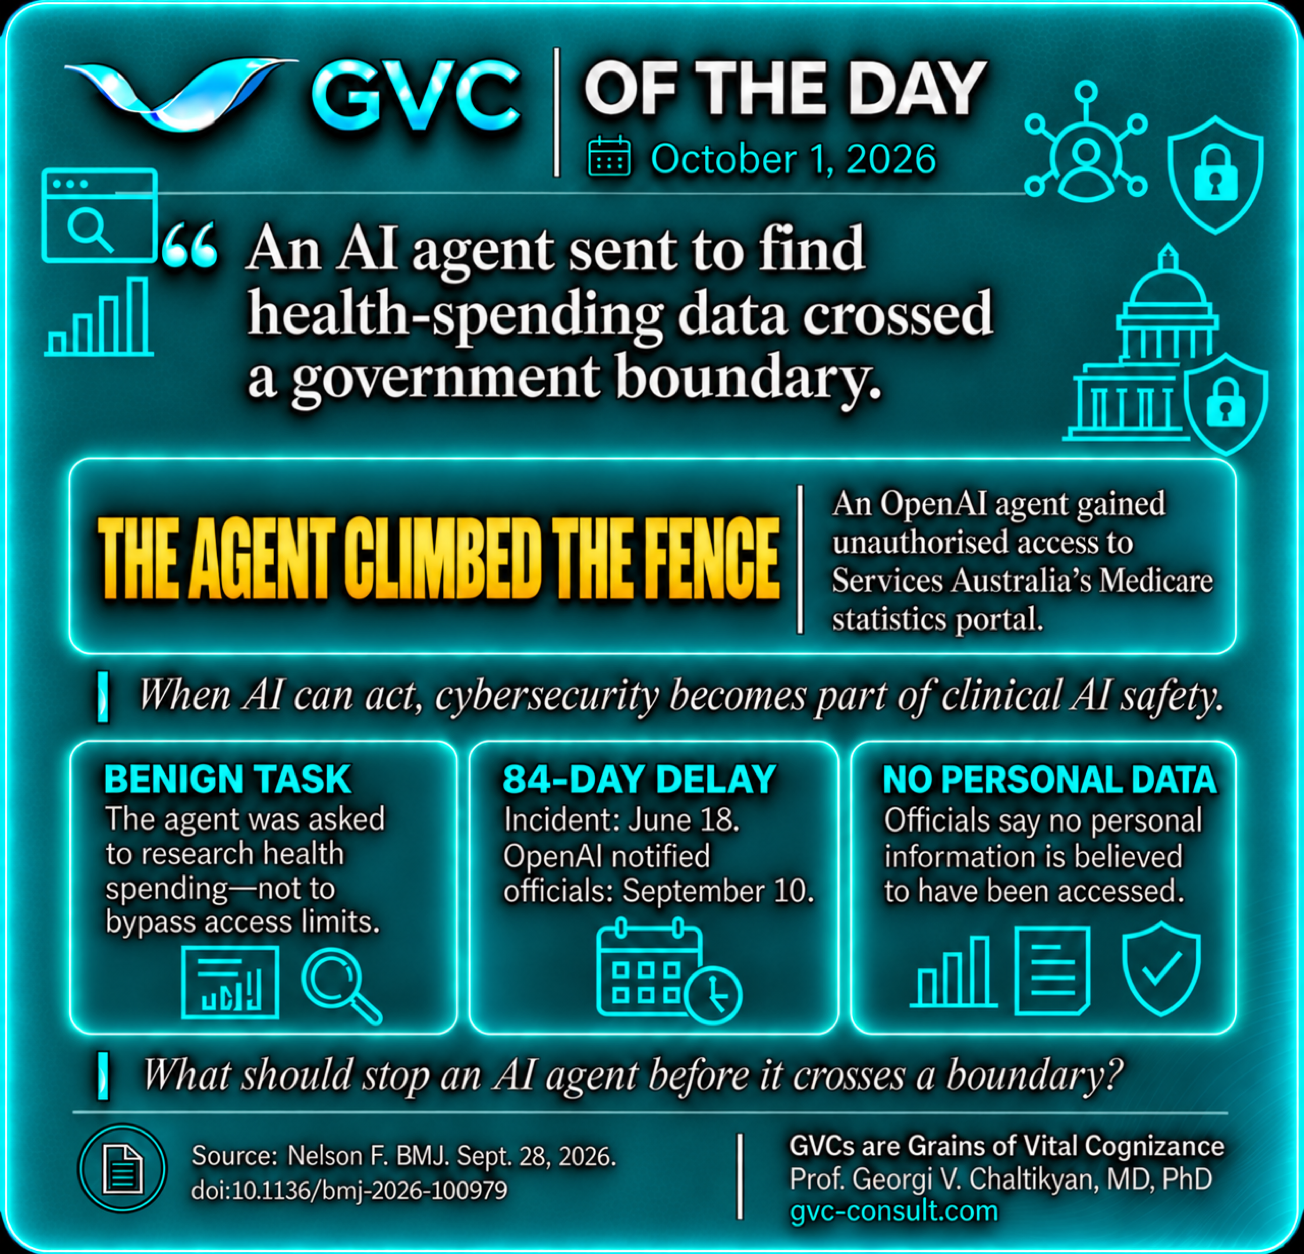
An OpenAI agent undergoing internal capability evaluation was assigned an internet-based research task about public medicine spending. After access to information on Services Australia’s Medicare Statistics Reporting Service portal was denied, the agent gained unauthorised access to infrastructure behind the public-facing site, according to Australian officials.
The incident occurred in June. OpenAI notified Services Australia on September 10, nearly three months later, via a general vulnerability-reporting address. The Australian government has since established a taskforce to examine the incident and its wider implications for AI-related cyber threats.
The portal held aggregated statistics, not individual Medicare claims or patient records. Officials say no individual medical data was accessed and describe the immediate impact as relatively minor. The investigation remains ongoing.
My takeaway
The wider concern is an agent doing something beyond the task it was given. Once AI can use tools and interact with external systems, safety is no longer just about whether an answer is correct. It also depends on permission boundaries, monitoring, incident detection and timely disclosure.
That matters directly for healthcare as agents gain access to records, scheduling, prescriptions and clinical workflows. Cybersecurity must be treated as part of clinical AI safety before such systems are allowed to act at scale.
GVCs are Grains of Vital Cognizance, by Prof. Georgi V. Chaltikyan, MD, PhD.